Client work · Recharge & bill payments
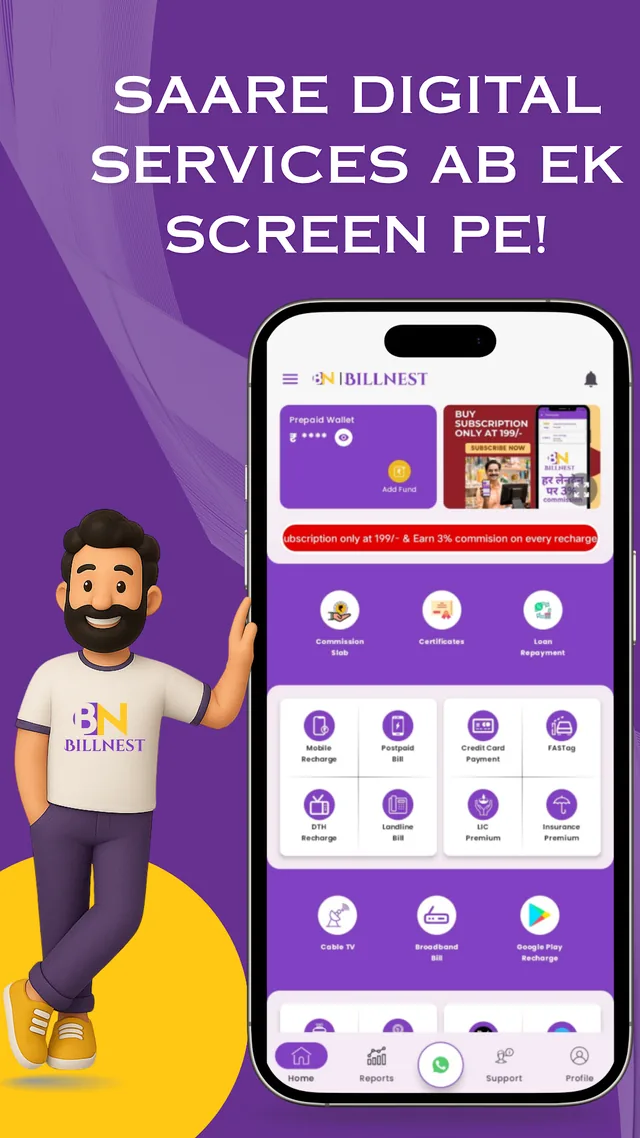
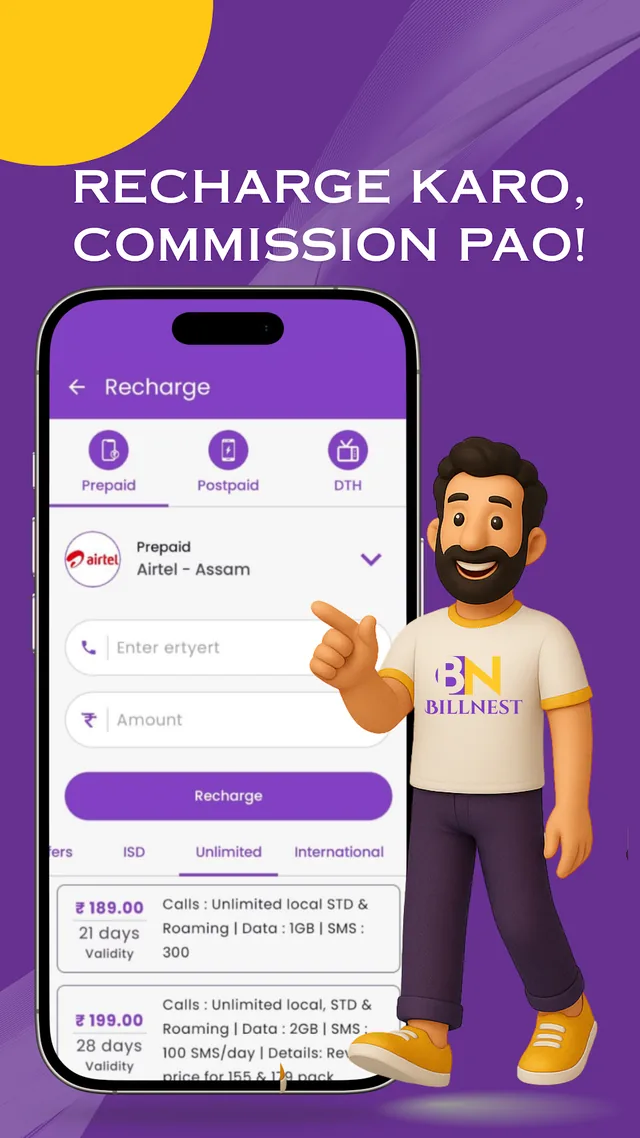
BillNest
A native Android app for recharge, bill payments, AEPS and BBPS, built with Kotlin and Jetpack Compose on a .NET backend.
Connect mobile apps, websites and business systems through APIs designed around the data they share. Cloudemy develops backend services with clear access rules, integration contracts and a release approach suited to the clients that depend on them.
A backend brings together API contracts, stored records, permissions and operational access. We scope those responsibilities alongside the mobile or web clients that use them.
Define what each client can request or change, including field meanings, pagination and useful errors. REST and GraphQL are options to assess against the consumers of the API. External integrations need provider documentation, suitable access and agreed behaviour when a request fails or arrives twice.
Node.js backend detailsOrders, accounts and employee records have relationships and business rules. We review query patterns, record ownership and consistency needs before choosing storage. Existing data needs a migration plan, validation and a way to review the result before a switch.
Identify users, roles and the operations each is permitted to perform. Authentication, authorization, input validation, secret handling and audit needs belong in the design. The depth of review and additional safeguards depend on the data and the product; no single checklist guarantees security.
Agree hosting, configuration, release access and the information needed to diagnose failures. The scope may include build automation, monitoring and backup or recovery responsibilities. Availability targets and deployment constraints are set for the system, rather than assumed to be universal.
The existing code, data model, integration needs and maintenance team guide the technology choice. The items below describe options to discuss; they are not a claim that every project uses the same infrastructure.
Mobile and web clients may change at different times. We plan compatibility and operational requirements around how the applications are used and maintained.
Agree which changes clients can tolerate and which need a migration or a new version. Define how older app releases are supported and how consumers will be informed of deprecations. Support periods are part of the project agreement.
Document request and response fields, authentication and the important workflows. An OpenAPI specification can support REST integration work. The required documentation, examples and test environment are agreed with the consuming teams.
Define error meanings, validation messages and how clients should recover. Retries, duplicate submissions and delayed callbacks need explicit treatment, especially where an operation creates an order or changes a transaction state.
Review authentication, role checks and permitted record changes before implementation. Include appropriate input validation, secret handling and logging. External provider permissions and security requirements are assessed with the integration scope.
Use verification appropriate to the API’s risks: contract behaviour, authorization, validation and important state transitions. Agree the checks, test data and release acceptance with the teams responsible for the clients and backend.
Identify who can deploy, where configuration is managed and what information helps diagnose a fault. Logging, health checks and recovery procedures need a scope and owner. Avoid recording sensitive customer data unnecessarily.
Integration discovery should identify which system owns a record, what happens during an outage and how a repeated request is handled. Those decisions affect the client interface as well as the backend. For a broader product scope, see custom software development and mobile app development.
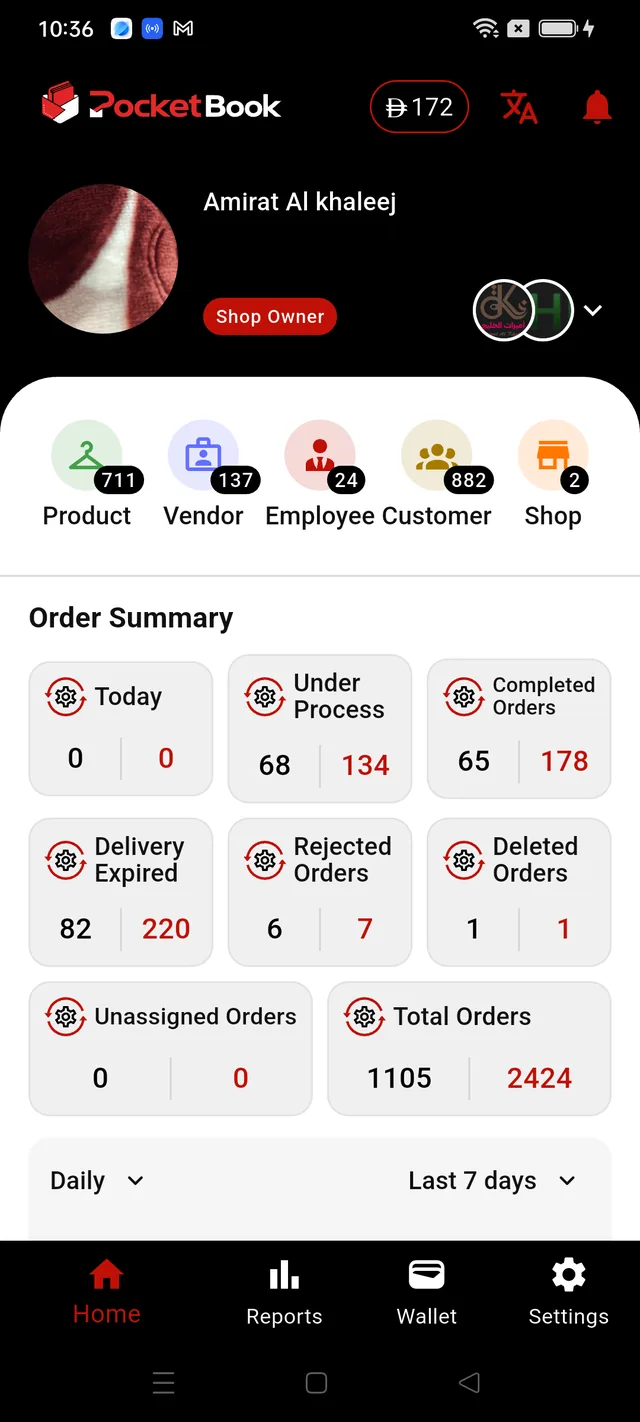
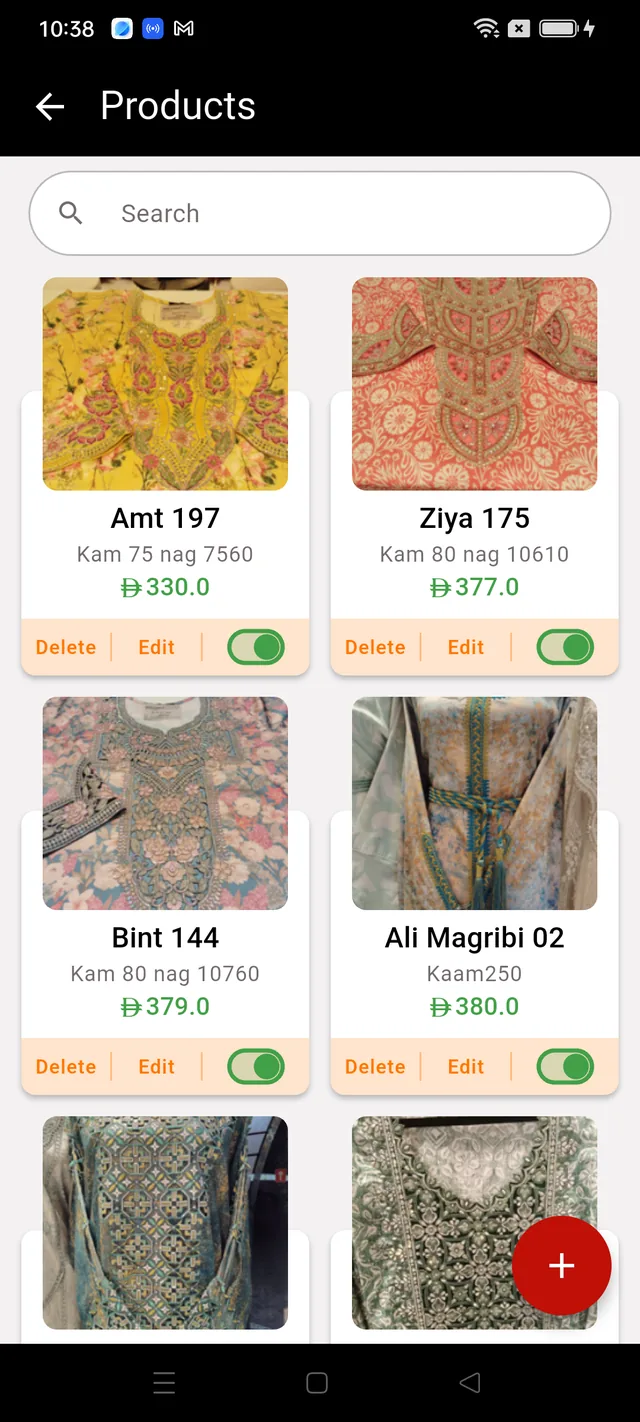
BillNest uses .NET behind its Android recharge and bill-payment app. PocketBook supports role-based business records and employee workflows. Their detailed integrations and operating requirements are product-specific.
Client work · Recharge & bill payments
A native Android app for recharge, bill payments, AEPS and BBPS, built with Kotlin and Jetpack Compose on a .NET backend.
Client work · Business management
Role-based product, order and employee workflows, redesigned for partners, counters and teams.
The scope can cover data models, APIs, business rules, permissions, external integrations and deployment preparation. Administrator tools and migration may also be needed. We distinguish the backend’s responsibilities from the mobile or web interface and document where the systems connect.
REST commonly suits resource and workflow APIs with well-defined operations. GraphQL can be useful when clients need flexible data selection. We consider the client applications, data relationships, authorization and operational requirements before recommending either; the choice is not a universal performance guarantee.
We review the records, relationships, query patterns and consistency requirements, along with any existing system. Storage options are assessed against those needs. A migration or shared-data integration also needs clear ownership and validation; the database name alone does not settle the architecture.
Start with the data, users and permitted operations. Authentication, authorization, validation and secrets need defined boundaries, and the logging and test scope should reflect the product’s risks. External providers may impose additional access or review requirements. We agree the controls and acceptance work for the engagement rather than promising a universal security outcome.
Yes. We can scope backend work alongside an existing mobile or web team. Repository access, current contracts, provider documentation and a suitable test environment help establish what can be extended. We agree compatibility, documentation and handover responsibilities before changing shared behaviour.
Tell us about the people who will use it, the work it needs to do and any systems it should connect to. We’ll discuss the scope, dependencies and next steps with you.